Audit Ready Workspace Permissions: 8 Step RBAC Runbook for IT Admins
Workspace permissions decide who can see, edit, publish, or manage a shared work environment, and the safest way to assign them is role-based access control (RBAC) built on least privilege, with groups doing the heavy lifting instead of individual user assignments. Get that structure right first, then worry about tools. Before you do anything else, pick one high-risk workspace and run a quick inventory of who currently has access and why.
TL;DR:
- Assigning permissions to groups rather than individuals simplifies access management and facilitates quick onboarding and offboarding of team members.
- Permission propagation delays, licensing restrictions, and nested group complexities can cause effective access to differ from the assigned roles, requiring regular audits.
- Reorganizations often leave excess permissions if roles are person-based; shifting to role-based group assignments ensures smoother transitions and clearer access control.
- Automated, continuous privilege reviews, including role and group membership audits, help prevent permission sprawl and maintain security compliance.
- Choosing a platform with straightforward, privacy-respecting permission models and transparent pricing can ease administration and reduce hidden access vulnerabilities.
Table of Contents
- What are workspace permissions, exactly?
- Assigning access: why groups beat individual grants
- Building an RBAC runbook that actually gets followed
- How do you verify who actually has access?
- Why permission changes don’t always take effect instantly
- Where RBAC principles come from and what backs them up
- Handling permission changes during restructuring
- Author perspective: what to do in the first 30 days
- A privacy-first option if you’re rebuilding your workspace setup
- Sources
- FAQ
What are workspace permissions, exactly?
Workspace permissions are the rules that determine which identities, whether that’s a person, a group, or a service account, can enter a workspace and what they’re allowed to do once inside. This differs from a plain “workspace vs project” distinction: a project is a container for tasks and deadlines, while a workspace is the access boundary wrapped around it, often holding several projects, boards, or files.
Confusion here is common because platforms use different words for near-identical concepts. Microsoft Fabric defines roles as Admin, Member, Contributor and Viewer, while HashiCorp’s Terraform Enterprise uses admin, write, plan and read tiers with support for custom permission sets. Google Workspace goes further still, letting admins build entirely custom admin roles rather than relying only on presets. The labels change, but the underlying job is the same: match access to what a person actually needs to do, nothing more.
Here’s how the common tiers typically map to capabilities:
- Admin — manages membership, changes roles, deletes the workspace, controls settings and integrations.
- Member — adds and removes content, invites others (in some platforms), edits shared items.
- Contributor — creates and edits content but usually can’t manage users or workspace-wide settings.
- Viewer — read-only access; can see boards, tasks, or reports but can’t change anything.
Some platforms complicate this with licensing tiers. A Contributor on a premium-capacity workspace might get abilities a Contributor on a free tier doesn’t, so always check whether a role’s real-world power depends on the license attached to the user, not just the role name.
Assigning access: why groups beat individual grants
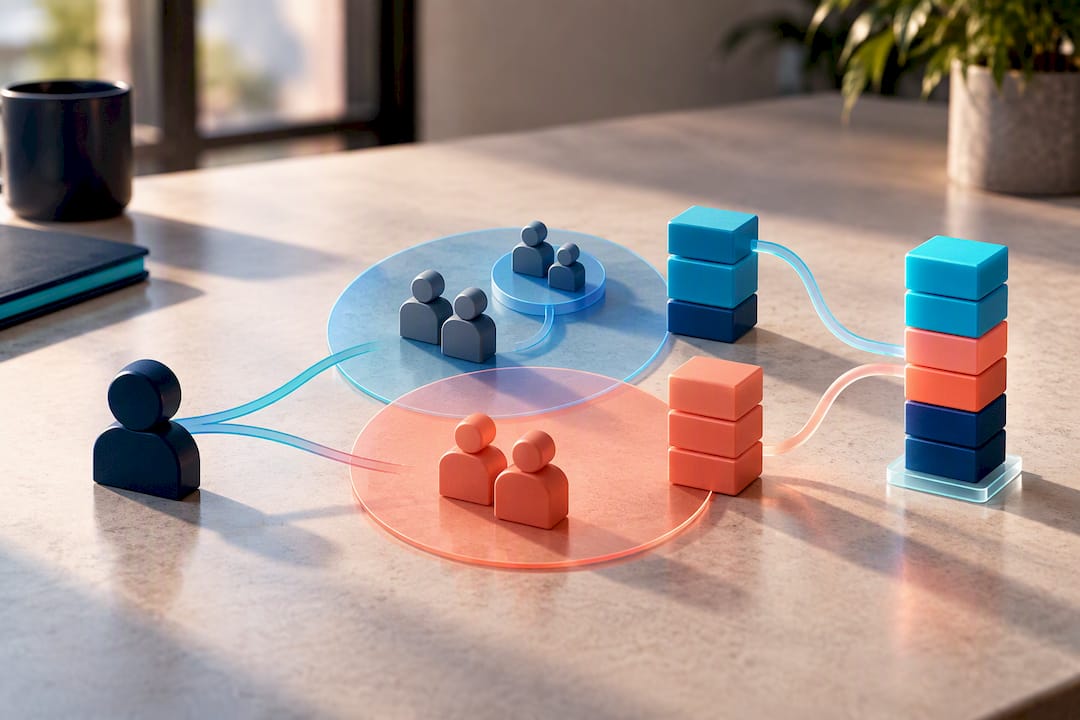
Assign permissions to groups, not individuals, whenever the platform allows it. Add a person to a group, and they inherit every permission tied to that group instantly, and when they leave the team, removing them from the group revokes access everywhere in one action instead of hunting through a dozen workspaces one by one.
The trade off is complexity you can’t see. Nested groups and overlapping memberships mean a user’s effective permission is often higher than anyone intended. Someone added to “Marketing Contributors” who is also a member of “All Staff Admins” through an old onboarding group ends up with admin rights nobody consciously granted them. This is one of the most overlooked group-based assignment risks: checking a user’s direct role tells you nothing about what they can actually do once inherited permissions stack up.
Platform limits add another wrinkle. Microsoft Fabric caps a workspace at 1,000 directly assigned users or groups, though a single group inside that cap can itself hold well over a thousand members. Google Workspace similarly caps some role assignments at 1,000 total assignments per role.
A practical sequence for any new team:
- Create a group per function, not per project (e.g. “Design Team,” not “Q3 Rebrand”).
- Assign the group to the workspace at the appropriate role tier.
- Add and remove individual users from the group as headcount changes, never re-touching the workspace itself.
Pro Tip: Before nesting one group inside another, ask what the combined permission would look like for the most junior member of the inner group. If that answer alarms you, don’t nest it.
Building an RBAC runbook that actually gets followed
A workable RBAC process doesn’t need to be elaborate, it needs to be repeatable. NIST’s guidance on role-based access control frames the goal clearly: permissions should follow job functions, not individual exceptions, because roles scale and one-off grants don’t.
Here’s a runbook that holds up under audit:
- Inventory every workspace and tag each by sensitivity (public, internal, confidential, restricted).
- Define roles by job function, not by person, and write down what each role can and can’t do.
- Map the minimum permission needed for each role to do its job, resisting the urge to round up “just in case.”
- Assign an approval owner for each workspace, someone accountable for who gets in.
- Prefer groups over direct assignment everywhere the platform supports it.
- Set expirations on temporary access rather than trusting someone to remember to revoke it.
- Test with a representative account before rolling a new role out broadly.
- Document every approval, even informal ones, so audits don’t rely on memory.
The elements worth automating first:
- Group membership syncs from your identity provider rather than manual adds.
- Expiration dates on any contractor or contractor-adjacent access.
- A recurring calendar reminder for privilege reviews, not an ad hoc one.
This mirrors NIST’s own emphasis on role hierarchies, mutually exclusive roles, and ongoing privilege review as the core mechanics that keep RBAC from decaying into permission sprawl.
How do you verify who actually has access?
Checking a user’s assigned role answers half the question. The other half is effective access, the sum of direct grants plus everything inherited through group membership, which is often broader than anyone intended.
A few concrete techniques help here:
- Pull a report that shows direct assignments and group-inherited permissions side by side, not just one or the other.
- Spot-check a handful of “ordinary” accounts quarterly, not just admin accounts, since over-permissioned regular users are the more common failure.
- Pair workspace-level roles with item-level controls like row-level security where the platform supports it, since workspace roles govern collaboration but don’t replace data-level restrictions.
- Log role changes and membership edits somewhere searchable, so an audit doesn’t depend on someone’s memory of who added whom.
A quarterly privilege review catches most drift before it becomes a real incident, and NIST’s own RBAC guidance treats revocation and audit as inseparable from the initial grant, not an afterthought bolted on later. Treat access review as part of the assignment process, not a separate compliance chore you get to when there’s time.
Why permission changes don’t always take effect instantly
A change that looks saved isn’t necessarily live. Microsoft states that permission changes in Fabric workspaces typically apply at the user’s next sign-in, not the moment you click save. Google documents a wider window: some admin privilege changes can take up to 24 hours to propagate across its systems.
License status matters just as much as role. A user with Contributor rights but no active license for a premium feature may see options they technically can’t use, or worse, lose creation ability entirely until licensing catches up.
When someone insists their new permission “isn’t working,” run this checklist before assuming it’s broken:
- Have them sign out and back in completely, not just refresh the page.
- Check for nested group membership that might be overriding the direct grant.
- Confirm the license tier attached to their account actually supports that role’s capabilities.
Pro Tip: Before escalating a “permission not working” ticket, ask when the change was made. If it was inside the last hour, it may simply not have propagated yet.
Where RBAC principles come from and what backs them up
The runbook above isn’t arbitrary; it’s a direct application of NIST’s role-based access control model, which recommends least privilege, role hierarchies, and mandatory review cycles specifically because ad hoc permission grants don’t scale. Platform documentation from Microsoft, Google, and HashiCorp confirms the same pattern across different products: role tiers, group-based assignment, and propagation delays are universal features of workspace access, not quirks of one vendor.
Some platforms apply this same logic to flexible workspaces, treating group-based access and data independence as defaults rather than add-ons.
Handling permission changes during restructuring
Team reshuffles break more access models than any other single event. When a person moves teams, gets promoted, or a department splits in two, permissions built around “who they are” survive the change badly; permissions built around “what job they do” survive it well.
The failure pattern is predictable: someone transfers from Sales to Product, keeps their old Sales workspace access “just in case,” and six months later nobody remembers why they can still see confidential pipeline data. Multiply that by a reorg affecting fifty people, and you’ve got a genuine audit headache.
The fix starts before the reorg, not after. If your roles are genuinely job-based rather than person-based, moving someone means removing them from the old functional group and adding them to the new one, a two-step action rather than a workspace-by-workspace hunt. This is exactly why group-based assignment earns its keep during organisational change, not just day-to-day administration.
For larger restructures, build a short transition checklist:
- Freeze new access grants during the active transition window to avoid compounding confusion.
- Run an access snapshot immediately before and after the change, so you can compare who had what.
- Set a 30-day expiration on any “temporary” access granted to smooth the transition, and actually enforce it.
- Notify workspace owners directly when their team’s membership shifts, since automated group syncs don’t always trigger a human review.
Mergers and acquisitions amplify all of this. Two organisations rarely share the same role taxonomy, so mapping “their Contributor” to “your Member” needs a deliberate decision, not an assumption that similarly named roles behave the same way.
Author perspective: what to do in the first 30 days
If you’re inheriting a messy permission structure, don’t try to fix everything at once. Spend week one on inventory, week two consolidating overlapping groups, and by week three run one real privilege review on your highest-risk workspace. Perfect governance can wait; a lightweight script that flags stale access can’t.
— Greg
A privacy-first option if you’re rebuilding your workspace setup
If you’re already rethinking how access works across your team, it’s worth choosing a platform that doesn’t complicate the model with hidden licensing tiers or vendor lock-in. Seven is built around flexible workspaces where role assignment stays straightforward, without the premium-capacity exceptions that trip up admins on some enterprise platforms.
Some platforms don’t mine user data or sell analytics, so the access granted stays private as configured. They support Excel import for onboarding existing task lists, open data export to avoid vendor lock-in, and built-in messaging alongside file attachments for teams that need collaboration without extra tools bolted on. That export capability matters more than it sounds. If a platform can’t hand your data back cleanly, your permission model is only ever as good as your relationship with that vendor.
Pricing is transparent: a fixed monthly cost for individuals and a per user per month cost for teams, both on the Individual and Teams plans. If you’re auditing your current workspace setup anyway, it’s a reasonable moment to compare what you’re paying against what you’re actually getting. Start a trial and see whether Seven’s permission model fits the way your team actually works.
Sources
- Roles in workspaces in Microsoft Fabric - Microsoft Learn
- Role-based access control (RBAC) features and motivations - NIST
- Assign specific admin roles | Google Workspace Help
- Workspace permissions | HashiCorp Terraform
FAQ
How do I change permissions in a shared workspace?
Open the workspace’s access or member management panel, usually called something like “Manage access,” and adjust the role assigned to the user or group. Microsoft notes that changes to Fabric workspace roles apply at the user’s next sign-in, not immediately, so don’t panic if someone reports no change within minutes.
How do I get access to a workspace I’m not currently in?
Request access from the workspace admin or approval owner, who adds you either directly or, more commonly, by placing you in the relevant group. Most platforms route this through a formal access request or invite flow rather than self-service joining, particularly for confidential workspaces.
How do I see who administers a workspace?
Check the workspace’s member or access list, which typically shows each person’s assigned role, including who holds Admin. If group membership is involved, you may need to check the group’s own membership list separately to see the full picture of who has administrative rights.
How do I edit permissions for an existing member?
Locate the member in the workspace’s access panel and change their assigned role tier directly, or move them between groups if access is group-based. Always check for nested group memberships first, since a direct role edit can be overridden by broader access inherited through another group.
What’s the difference between a workspace and a project?
A workspace is the access boundary controlling who can enter and what they can do; a project is a container for tasks, deadlines, and deliverables that usually lives inside a workspace. Platforms like Seven organise multiple projects within one flexible workspace, keeping permission management separate from day-to-day task structure.